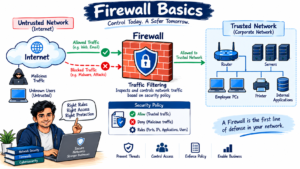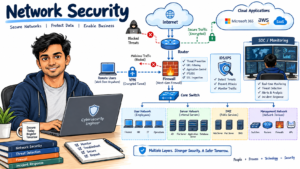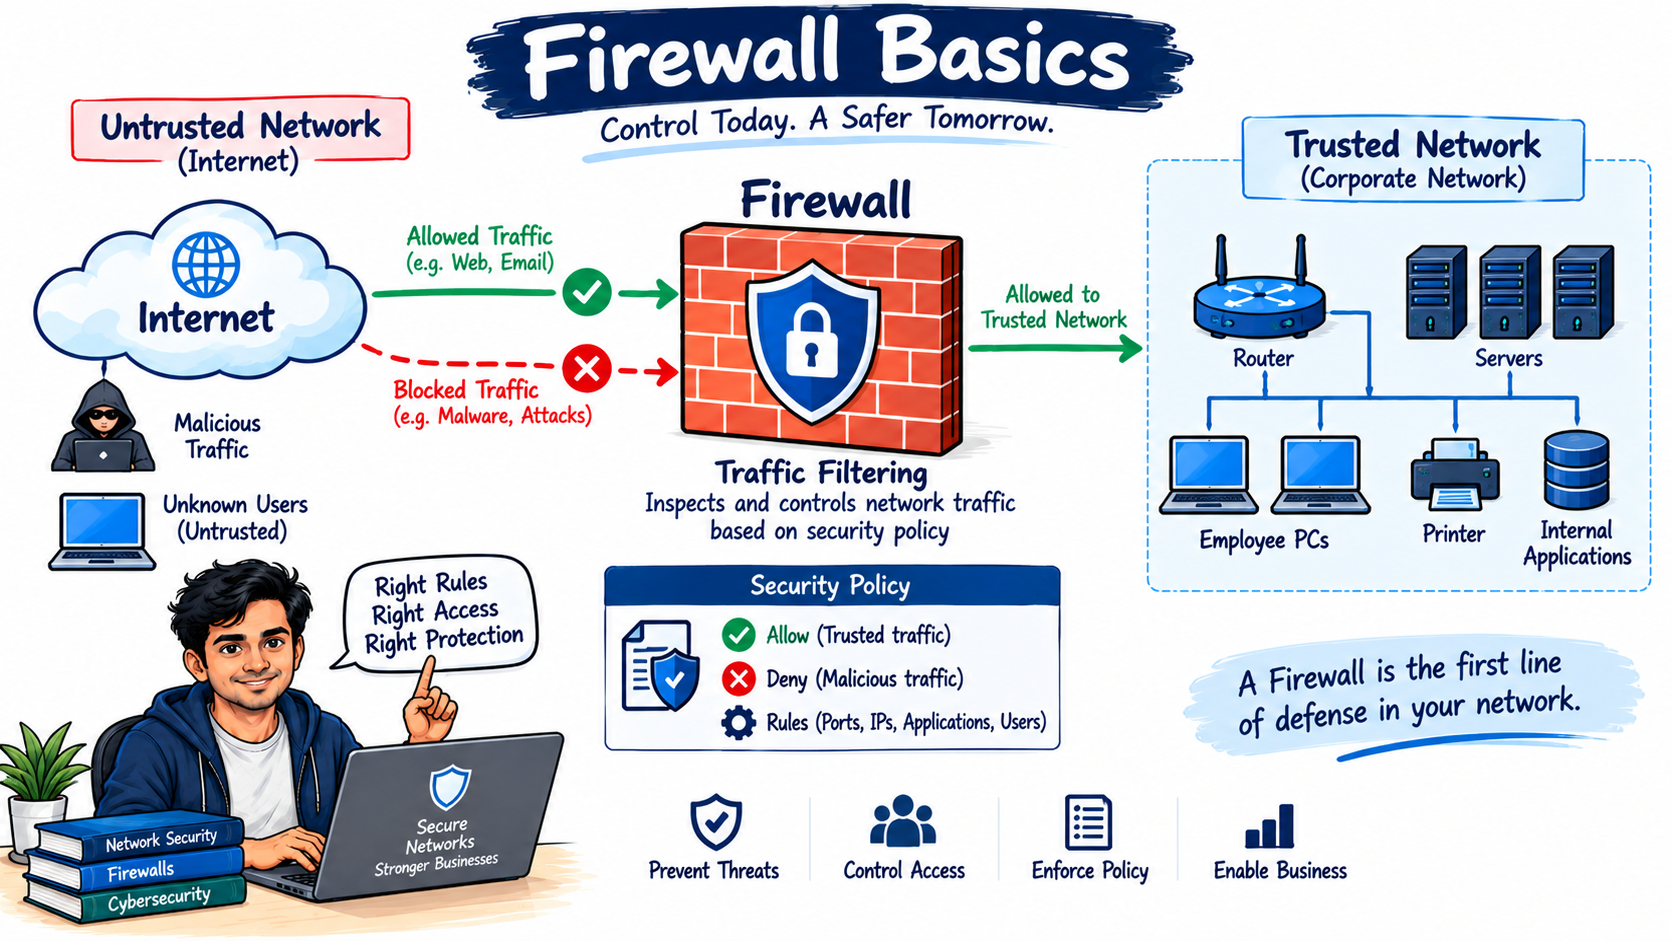
If you are preparing for a cybersecurity, network security, SOC, network administrator, or firewall administrator interview, firewall concepts are important. Interviewers commonly ask about firewall types, security policies, NAT, VPNs, DMZ, logging, troubleshooting, and real-world traffic scenarios.
This guide covers 50 firewall interview questions and answers, from basic concepts to advanced troubleshooting scenarios.
Basic Firewall Interview Questions
1. What is a firewall?
A firewall is a security system that monitors and controls network traffic based on predefined security policies.
It can allow legitimate traffic and block unauthorized traffic between networks or systems.
For example, an organization may configure a firewall to allow employees to access websites over HTTPS while blocking unauthorized inbound connections from the Internet.
Simple example:
Internet
    |
    v
 Firewall
    |
    v
Corporate Network
The firewall acts as a security control point between the two networks.
Firewall Interview Questions
2. What is the main purpose of a firewall?
The main purpose of a firewall is to control network traffic and prevent unauthorized communication.
A firewall can:
- Allow or block network connections
- Restrict access based on IP addresses and ports
- Control applications
- Perform NAT
- Create network segmentation
- Support VPN connections
- Log network traffic
- Integrate with security services such as IPS and threat prevention
For example, a firewall can allow TCP 443 from employee networks to the Internet while blocking unnecessary inbound connections.
3. How does a firewall work?
A firewall receives network traffic and compares it against its configured security policies.
It can evaluate information such as:
- Source IP address
- Destination IP address
- Source port
- Destination port
- Protocol
- Application
- User identity
- Security zone
If the traffic matches an allow rule, the firewall permits it. If it matches a deny rule, the firewall blocks it.
Example:
Source: 10.10.10.50
Destination: Web Server
Protocol: TCP
Port: 443
Action: Allow
The firewall permits the HTTPS connection if this traffic matches the configured policy.
Firewall Interview Questions
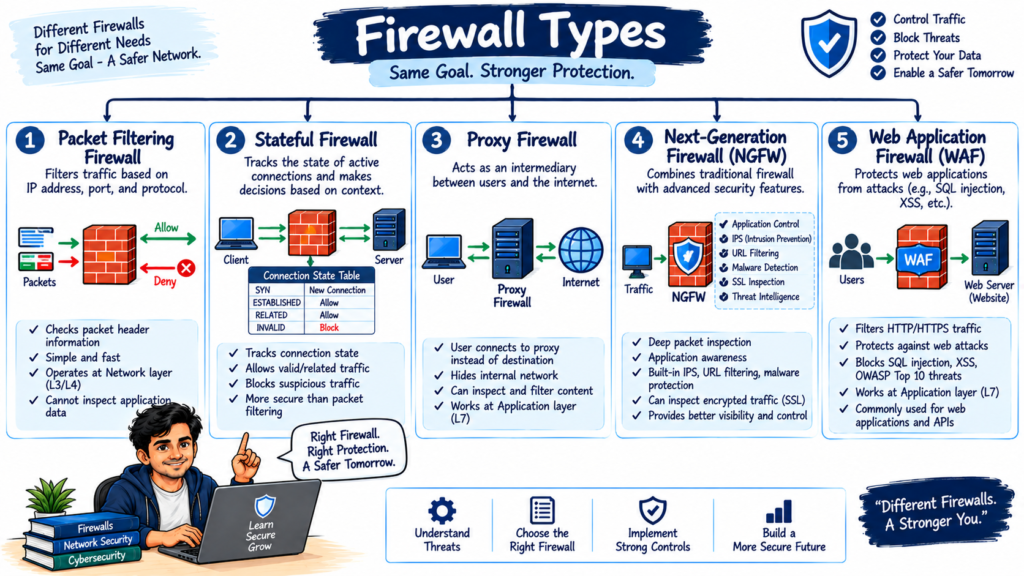
4. What are the different types of firewalls?
Common firewall types include:
- Packet-filtering firewall
- Stateful firewall
- Proxy firewall
- Next-Generation Firewall (NGFW)
- Web Application Firewall (WAF)
- Host-based firewall
- Cloud firewall
The major difference is how much context the firewall can inspect.
For example, a traditional firewall may primarily evaluate IP addresses and ports, while an NGFW can identify applications and users and inspect traffic for threats.
5. What is a packet-filtering firewall?
A packet-filtering firewall examines network packets based on packet-header information.
It can make decisions using:
- Source IP
- Destination IP
- Protocol
- Source port
- Destination port
For example:
Source: 10.10.10.0/24
Destination: Any
Protocol: TCP
Destination Port: 443
Action: Allow
This rule allows HTTPS traffic from the specified network.
Packet filtering is relatively simple because it does not necessarily inspect the contents of the application traffic.
Firewall Interview Questions
6. What is a stateful firewall?
A stateful firewall keeps track of active network connections.
For example, when a client starts a TCP connection to a web server, the firewall records information about that session.
Client → Firewall → Web Server
           |
           └── Session State
When the response comes back, the firewall can determine whether it belongs to an established connection.
This allows the firewall to make decisions based on connection state rather than treating every packet independently.
7. What is a stateless firewall?
A stateless firewall evaluates each packet independently.
It does not maintain connection state in the same way as a stateful firewall.
For example, a stateless rule could allow:
Source: 10.10.10.0/24
Destination: 192.168.1.10
Protocol: TCP
Port: 443
Action: Allow
Each packet is evaluated against the configured rules.
8. What is a Next-Generation Firewall?
A Next-Generation Firewall (NGFW) provides traditional firewall functionality along with additional security capabilities.
Depending on the product, an NGFW may provide:
- Application identification
- User-based policies
- Intrusion Prevention System
- SSL/TLS inspection
- URL filtering
- Malware detection
- Threat intelligence
- Advanced logging
For example, instead of simply allowing TCP 443, an NGFW may identify the application generating the traffic and apply a policy based on that application.
Firewall Interview Questions
9. What is the difference between a firewall and antivirus?
A firewall primarily controls network communication, while antivirus software primarily detects and prevents malicious software on systems.
| Firewall | Antivirus |
|---|---|
| Controls network traffic | Detects malicious software |
| Applies network security policies | Scans files and processes |
| Blocks unauthorized connections | Detects malware |
| Can protect network boundaries | Primarily protects endpoints |
They solve different security problems and are commonly used together.
10. What is a network firewall?
A network firewall is a security device or software system that controls traffic between networks.
For example:
Internet
   |
Firewall
   |
DMZ
   |
Internal Network
The firewall can apply different security policies to traffic moving between these network zones.
Firewall Rules and Policies
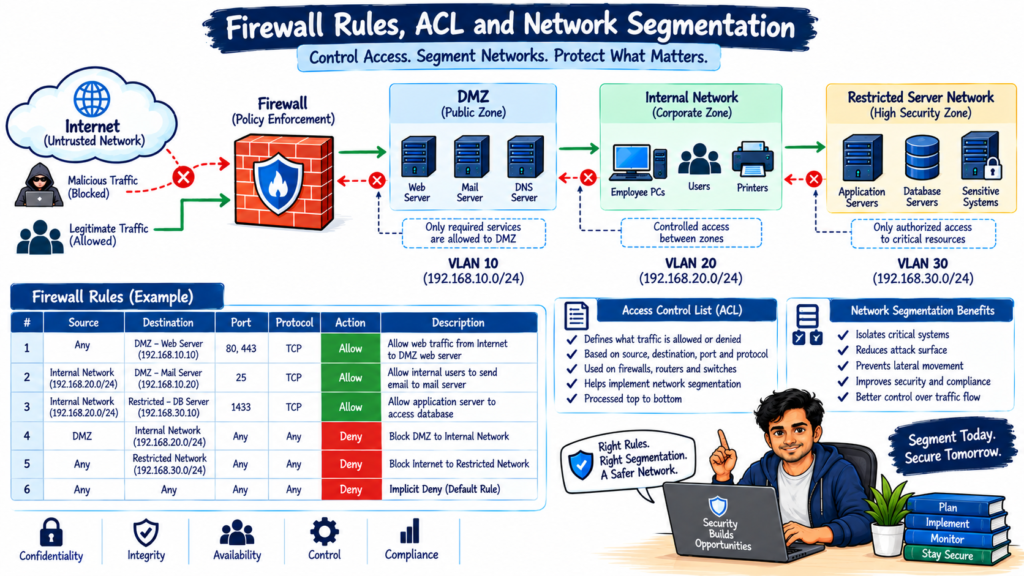
11. What is a firewall rule?
A firewall rule defines how specific network traffic should be handled.
A rule can contain:
- Source
- Destination
- Protocol
- Port
- Application
- User
- Action
For example:
Source: Employee Network
Destination: Internet
Service: HTTPS
Action: Allow
The firewall evaluates traffic against these rules and takes the configured action.
12. What is the difference between deny and reject?
Both deny and reject prevent traffic from being allowed, but their behavior can differ.
Deny: The firewall drops the traffic without necessarily sending a response.
Reject: The firewall drops the traffic and may send a response indicating that the connection was refused or unreachable.
The exact behavior depends on the firewall vendor and configuration.
Firewall Interview Questions
13. What is an implicit deny rule?
An implicit deny is the default behavior that blocks traffic when no configured rule explicitly permits it.
For example:
Rule 1: Allow HTTPS
Rule 2: Allow DNS
Rule 3: Allow SSH from Admin Network
Default: Deny
If traffic does not match Rules 1, 2, or 3, it is denied.
This helps implement a default-deny security model.
14. What is the principle of least privilege in firewall rules?
The principle of least privilege means allowing only the traffic that is required.
For example, instead of allowing:
Source: Any
Destination: Any
Service: Any
Action: Allow
a more restrictive policy would be:
Source: Admin Network
Destination: Management Server
Service: HTTPS
Action: Allow
This reduces unnecessary network exposure.
Firewall Interview Questions
15. What is firewall rule ordering?
Firewall rule ordering determines which policy is evaluated first.
Many firewalls evaluate rules from top to bottom and apply the first matching rule.
For example:
Rule 1:
Allow 10.10.10.50 → Server TCP/443

Rule 2:
Deny 10.10.10.0/24 → Server
Traffic from 10.10.10.50 matches Rule 1 first and is allowed.
Therefore, incorrect rule ordering can cause unexpected access.
Firewall Interview Questions
16. What happens when two firewall rules conflict?
The result depends on the firewall’s rule-processing logic.
Many firewalls use a first-match approach, meaning the first matching rule determines the action.
For example:
Rule 1: Allow 10.10.10.50 → Server TCP/443
Rule 2: Deny 10.10.10.0/24 → Server
The traffic from 10.10.10.50 would normally be allowed because Rule 1 is evaluated first.
During troubleshooting, always check the rule order and the actual rule that matched the traffic.
17. What is a firewall object?
A firewall object is a reusable definition representing a network resource.
Common objects include:
- Host objects
- Network objects
- Service objects
- Address groups
- Service groups
For example:
Web_Server = 10.10.10.20You can then use Web_Server in multiple firewall policies instead of entering the IP address repeatedly.
Firewall Interview Questions
18. What is a service object?
A service object defines a protocol and port used by a network service.
For example:
HTTPS
Protocol: TCP
Port: 443
Another example:
SSH
Protocol: TCP
Port: 22
Service objects make firewall policies easier to read and manage.
Firewall Interview Questions
19. What is a firewall ACL?
ACL stands for Access Control List.
An ACL contains rules that determine whether traffic should be permitted or denied.
For example:
Permit TCP 10.10.10.0/24 → 172.16.10.10:443
Deny IP Any → Any
ACLs are commonly used on firewalls and network devices to control access.
Firewall Interview Questions
20. What is a default-deny policy?
A default-deny policy blocks traffic unless it is explicitly permitted by a security rule.
For example:
Allow required traffic
        ↓
Log relevant traffic
        ↓
Deny everything else
This reduces unnecessary exposure and follows the principle of least privilege.
Ports and Protocols
21. What is the difference between TCP and UDP?
TCP is connection-oriented and provides reliable, ordered data delivery.
UDP is connectionless and has lower protocol overhead but does not provide TCP’s built-in reliability mechanisms.
Examples:
| Protocol | Common Port | Example |
|---|---|---|
| HTTP | 80/TCP | Web traffic |
| HTTPS | 443/TCP | Secure web traffic |
| SSH | 22/TCP | Secure administration |
| DNS | 53/TCP/UDP | Name resolution |
| DHCP | 67/68 UDP | IP address assignment |
22. What is port 80?
TCP port 80 is commonly used by HTTP.
HTTP normally does not provide encryption for the application data.
Example:
Client → TCP/80 → Web ServerToday, many public websites redirect HTTP traffic to HTTPS.
23. What is port 443?
TCP port 443 is commonly used for HTTPS.
HTTPS uses TLS to protect application traffic between the client and server.
Example:
Client → TCP/443 → Web ServerFirewall administrators commonly need to allow TCP 443 for web access.
Firewall Interview Questions
24. What is port 22?
TCP port 22 is commonly used by SSH.
SSH provides secure remote administration of systems.
Because SSH provides administrative access, organizations commonly restrict port 22 to trusted management networks rather than exposing it broadly to the Internet.
Firewall Interview Questions
25. Why is DNS important when configuring firewall policies?
DNS converts domain names into IP addresses.
For example:
www.example.com
       ↓
      DNS
       ↓
93.184.216.34
If DNS traffic is blocked, users may be unable to resolve domain names even though other network connectivity is working.
When troubleshooting Internet access, check both DNS resolution and direct IP connectivity.
NAT and Firewall Interview Questions
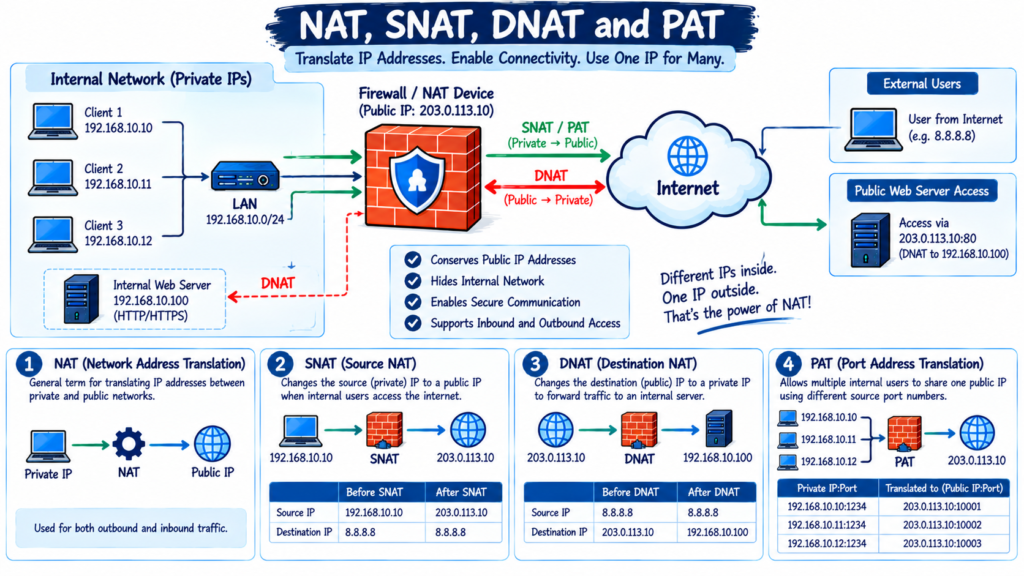
26. What is NAT?
NAT stands for Network Address Translation.
NAT changes IP address information as traffic passes through a network device.
A common use case is allowing private internal addresses to access the Internet using public IP addresses.
Example:
10.10.10.20
     |
 Firewall
     |
203.0.113.10
     |
 Internet
27. What is SNAT?
SNAT stands for Source Network Address Translation.
SNAT changes the source IP address of a packet.
For example:
Before NAT:
Source = 10.10.10.20

After SNAT:
Source = 203.0.113.10
SNAT is commonly used for outbound Internet traffic from private networks.
Firewall Interview Questions
28. What is DNAT?
DNAT stands for Destination Network Address Translation.
DNAT changes the destination IP address of traffic.
For example:
Internet
    |
203.0.113.10
    |
 Firewall
    |
10.10.10.20
Web Server
A public IP can be translated to an internal server.
This is commonly used for publishing services through a firewall.
Firewall Interview Questions
29. What is PAT?
PAT stands for Port Address Translation.
PAT allows multiple private IP addresses to share a public IP address by using different source port numbers.
For example:
10.10.10.10:50001 ─┐
10.10.10.11:50002 ─┼→ 203.0.113.10
10.10.10.12:50003 ─┘
The firewall tracks the translated sessions so that return traffic reaches the correct internal client.
30. What is the difference between NAT and PAT?
NAT translates IP addresses.
PAT also uses port numbers to allow multiple private systems to share a public IP address.
A simple way to remember it:
NAT = Address Translation

PAT = Address + Port Translation
PAT is commonly used for Internet access in enterprise and home networks.
VPN and Firewall
31. What is a VPN?
VPN stands for Virtual Private Network.
A VPN creates a secure communication channel between endpoints or networks over an untrusted network such as the Internet.
Common VPN types include:
- Site-to-site VPN
- Remote-access VPN
For example, a branch office can use a VPN tunnel to securely communicate with a corporate data center.
Firewall Interview Questions
32. What is a site-to-site VPN?
A site-to-site VPN securely connects two networks.
For example:
Branch Network
      |
   Firewall
      |
   VPN Tunnel
      |
   Firewall
      |
Head Office
IPsec is commonly used for site-to-site VPNs.
Users inside each network can communicate through the VPN according to the configured security policies.
Firewall Interview Questions
33. What is an IPsec VPN?
IPsec is a set of protocols used to secure IP communication.
It can provide:
- Confidentiality through encryption
- Authentication
- Data integrity
- Anti-replay protection
IPsec is commonly used for site-to-site VPN connections.
Firewall Interview Questions
34. What is an SSL/TLS VPN?
An SSL/TLS VPN uses TLS to establish secure remote connectivity.
It is commonly used for remote users who need access to corporate applications or network resources.
The exact architecture depends on the VPN product and deployment model.
Advanced Firewall Interview Questions
35. What is a DMZ?
DMZ stands for Demilitarized Zone.
A DMZ is a separate network segment used for systems that need controlled communication with external networks.
Typical DMZ systems include:
- Web servers
- Reverse proxies
- Mail gateways
- Public DNS servers
Example:
Internet
    |
 Firewall
    |
   DMZ
    |
Web Server
The firewall can restrict communication between the DMZ and internal network.
Firewall Interview Questions
36. Why is network segmentation important for firewalls?
Network segmentation divides a network into separate security zones.
For example:
Internet
   |
Firewall
   |
DMZ
   |
Internal Network
   |
Restricted Server Network
The firewall can control traffic between each zone.
If a server in one zone is compromised, segmentation can help limit unnecessary access to other zones.
Firewall Interview Questions
37. What is a WAF?
WAF stands for Web Application Firewall.
A WAF is designed to protect web applications by inspecting HTTP and HTTPS traffic.
It can help detect and block attacks such as:
- SQL injection
- Cross-site scripting
- Malicious HTTP requests
- Certain application-layer attacks
A WAF and network firewall serve different purposes. A network firewall controls broader network traffic, while a WAF focuses on web application traffic.
38. What is firewall logging?
Firewall logging records information about network connections and security events.
A firewall log may contain:
Timestamp
Source IP
Destination IP
Source Port
Destination Port
Protocol
Action
Rule ID
For example:
10.10.10.20 → 172.16.10.50
TCP/443
Action: Deny
Rule: 105
Firewall logs are useful for troubleshooting, incident investigation, and security monitoring.
Firewall Interview Questions
39. What is firewall log analysis?
Firewall log analysis involves examining firewall events to understand network behavior and identify potential security issues.
For example, if a server suddenly generates thousands of denied outbound connections, an administrator can investigate the destination addresses, ports, frequency, and associated processes.
Firewall logs can also be forwarded to a SIEM for centralized monitoring and correlation.
Firewall Interview Questions
40. What is firewall high availability?
Firewall high availability, or HA, provides redundancy by using multiple firewall devices.
A common design is:
             Internet
                 |
        +--------+--------+
        |                 |
    Firewall 1        Firewall 2
        |                 |
        +--------+--------+
                 |
          Internal Network
If one firewall becomes unavailable, the other can continue handling traffic, depending on the HA architecture.
Firewall Interview Questions
Scenario-Based Firewall Interview Questions
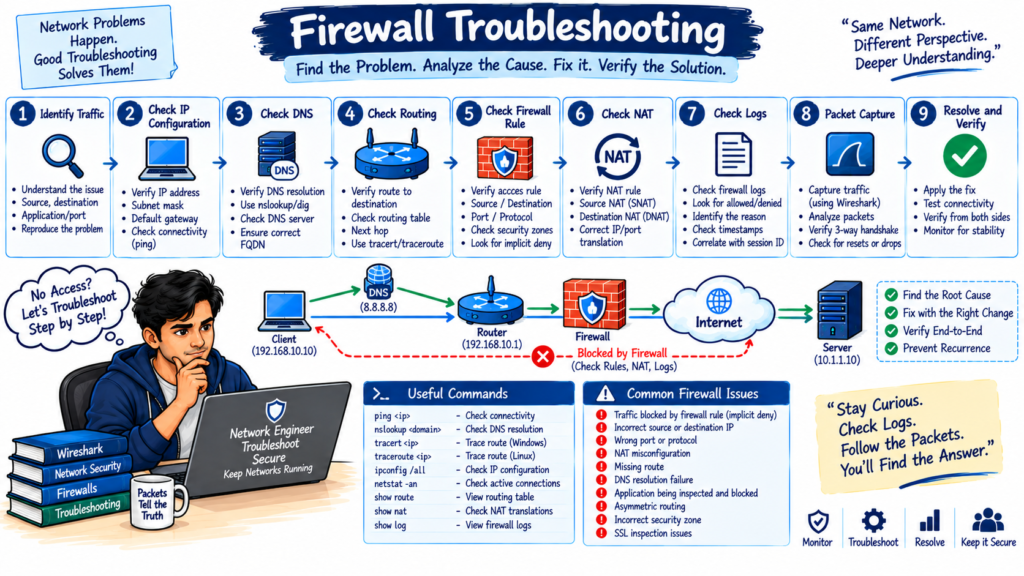
41. A user cannot access a website. How would you troubleshoot it?
I would troubleshoot the complete traffic path instead of immediately changing the firewall rule.
First, I would check:
- Is the user connected to the network?
- Can the user resolve the domain using DNS?
- What IP address does the domain resolve to?
- Can the user reach TCP port 443?
- Is the firewall allowing the connection?
- Which firewall rule matches the traffic?
- Are URL filtering or application controls blocking it?
- Is SSL inspection involved?
- Does the issue affect one user or multiple users?
- Do firewall logs show the connection being denied?
Tools such as ping, nslookup/dig, Test-NetConnection, traceroute, firewall logs, and packet captures can help isolate the issue.
Firewall Interview Questions
42. A server cannot access the Internet. What would you check?
I would check the network path in this order:
Server
  ↓
Default Gateway
  ↓
Routing
  ↓
Firewall
  ↓
NAT
  ↓
Internet
I would verify:
- IP configuration
- Default gateway
- DNS
- Routing table
- Firewall policy
- NAT configuration
- Security zones
- Destination ports
- Firewall logs
For example, if the server can reach an Internet IP but cannot resolve domain names, DNS is a more likely problem than the firewall’s HTTPS policy.
Firewall Interview Questions
43. A firewall is blocking legitimate traffic. How would you troubleshoot it?
I would first identify the exact traffic flow:
Source
   ↓
Destination
   ↓
Protocol
   ↓
Port
   ↓
Firewall Policy
Then I would check the firewall logs to determine which rule processed the traffic.
I would verify:
- Source address
- Destination address
- Source zone
- Destination zone
- Port
- Protocol
- NAT
- Rule order
- Security profiles
Once the cause is confirmed, I would make the minimum required policy change through the organization’s change-management process.
Firewall Interview Questions
44. Users can access HTTP but not HTTPS. What would you check?
I would focus on TCP 443 and TLS-related controls.
I would check:
- Firewall policy for TCP 443
- DNS resolution
- Routing
- NAT
- SSL/TLS inspection
- Certificate validation
- Proxy configuration
- Firewall logs
- Destination server availability
A packet capture can also help determine whether the TCP connection is failing or whether the problem occurs later during the TLS handshake.
45. How would you troubleshoot a firewall rule that is not working?
I would verify the actual traffic parameters against the firewall policy.
I would check:
- Source IP
- Destination IP
- Source zone
- Destination zone
- Protocol
- Destination port
- NAT
- Rule order
- Routing
- Security profiles
- Firewall logs
The key is to identify which rule actually matches the traffic.
If the expected rule is not matching, I would investigate object definitions, zones, NAT, and rule ordering.
Firewall Interview Questions
46. How would you determine whether a firewall is causing network latency?
I would compare latency before and after the firewall in the traffic path.
For example:
Client
  |
Router
  |
Firewall
  |
Internet
I would check:
- Firewall CPU utilization
- Memory utilization
- Concurrent sessions
- Connection rate
- Throughput
- Packet drops
- Interface errors
- SSL inspection load
- IPS processing
- Logging load
I would also use packet captures to determine whether delays are caused by the firewall or another device in the path.
47. What is asymmetric routing, and why can it cause firewall problems?
Asymmetric routing occurs when traffic takes different paths in each direction.
For example:
Client → Firewall A → Server

Server → Firewall B → Client
A stateful firewall may expect both directions of a connection to pass through the same firewall or firewall cluster.
If the return traffic reaches a different device without the required session state, the firewall may drop the traffic.
During troubleshooting, I would check routing tables, firewall session tables, and packet captures.
Firewall Interview Questions
48. What is a firewall session table?
A firewall session table contains information about active network connections.
A session may contain:
- Source IP
- Destination IP
- Source port
- Destination port
- Protocol
- Connection state
- Timeout information
- NAT information
For example:
10.10.10.20:51000
        ↓
203.0.113.50:443
        ↓
TCP Established
Session information is useful when troubleshooting connection failures, NAT issues, and stateful firewall behavior.
49. What would you do if firewall CPU utilization reaches 100%?
I would first identify what is consuming the firewall resources.
I would check:
- Traffic volume
- Concurrent sessions
- New connection rate
- SSL inspection
- IPS processing
- Threat detection activity
- Logging volume
- Interface utilization
- Recent configuration changes
- Potential abnormal traffic
I would also review monitoring data and vendor-specific diagnostics.
I would avoid restarting the firewall as the first troubleshooting step because that can interrupt active traffic and remove useful diagnostic information.
Firewall Interview Questions
50. How would you design a secure firewall architecture for an enterprise?
I would start by identifying the required traffic flows and separating systems into appropriate security zones.
A simplified architecture could look like this:
                         Internet
                            |
                     Edge Firewall
                            |
              +-------------+-------------+
              |                           |
             DMZ                    Internal Firewall
              |                           |
        Public Services              User Network
                                          |
                                   Server Network
                                          |
                                  Restricted Network
                                          |
                                     Databases
I would consider:
- Least-privilege firewall policies
- Default-deny rules
- Network segmentation
- DMZ architecture
- Firewall high availability
- NAT
- VPN
- Threat prevention
- Logging
- SIEM integration
- Administrative access controls
- Regular firewall rule reviews
- Configuration backups
- Change management
- Monitoring and alerting
The exact architecture would depend on the organization’s applications, network design, compliance requirements, and security policies.
Quick Revision: Firewall Interview Topics
Before your interview, make sure you can explain these topics in your own words:
| Topic | Key concept |
|---|---|
| Firewall | Controls network traffic |
| Stateful Firewall | Tracks connections |
| Stateless Firewall | Evaluates packets independently |
| NGFW | Advanced application and threat controls |
| ACL | Traffic access rules |
| Rule Ordering | Determines policy evaluation |
| Implicit Deny | Blocks unmatched traffic |
| Least Privilege | Allow only required traffic |
| NAT | Translates addresses |
| SNAT | Translates source address |
| DNAT | Translates destination address |
| PAT | Uses ports for address sharing |
| DMZ | Isolated zone for controlled external access |
| VPN | Secure network connectivity |
| IPsec | Secures IP communication |
| WAF | Protects web applications |
| Firewall Logs | Records traffic/security events |
| SIEM | Centralized security monitoring |
| HA | Provides firewall redundancy |
| Segmentation | Separates network security zones |
| Asymmetric Routing | Different forward and return paths |
| Session Table | Tracks active connections |
| Troubleshooting | Follow the traffic flow |
Official Cybersecurity Resources
- NIST Cybersecurity Framework
NIST Cybersecurity Framework - CISA Cybersecurity Best Practices
CISA Cybersecurity Best Practices - MITRE ATT&CK
MITRE ATT&CK
Network and Security Standards
- IETF RFC Editor
IETF RFC Editor - OWASP
OWASP Foundation - OWASP Top 10
OWASP Top 10
Related Cybersecurity and Networking Guides
- What is Firewall in Cybersecurity? Types, Examples and How it Works in 2026
https://technaga.com/firewall-in-cybersecurity-types-examples-explained/ - NGFW Guide: 5 Critical Reasons Your Firewall is Failing
https://technaga.com/ngfw-vs-traditional-firewall/ - Network Devices: 9 Essential Types & OSI Model Guide
https://technaga.com/network-devices-functions-osi-layers/ - Network Protocols and Ports: 10 Critical Security Facts
https://technaga.com/network-protocols-ports-security-guide/ - OSI Model Guide: 7 Powerful Layers Every Engineer Must Know
https://technaga.com/osi-model-7-layers-troubleshooting-guide/ - TCP/IP Model for Security Analysts
https://technaga.com/tcp-ip-model-security-guide/ - 3-Way Handshake Troubleshooting: Critical Guide for Security Analysts
https://technaga.com/tcp-3-way-handshake-security-analyst-guide/ - Network Segmentation Explained with Real-World Example
https://technaga.com/network-segmentation-guide-ransomware-prevention/ - Complete Network Security Basics Guide for Beginners 2026
https://technaga.com/what-is-networks-and-network-security-basics-2026/ - Security Information and Event Management: Complete SIEM Guide 2026
https://technaga.com/security-information-and-event-management-2026/
Disclaimer: The information provided in this article, including the Firewall Interview Questions and answers, is intended for educational and interview-preparation purposes only. Firewall technologies, configurations, commands, and security policies may vary between vendors and network environments. Always refer to the official documentation of your firewall platform and follow your organization’s security and change-management procedures before making any configuration changes. Tech Naga does not accept responsibility for service interruptions, security issues, data loss, or other consequences resulting from the use of information provided in this article.